Home
» News
»
Zero-Knowledge Proofs in Q4 2026: Scalability Is Maturing, Privacy Is Becoming Practical
Zero-Knowledge Proofs in Q4 2026: Scalability Is Maturing, Privacy Is Becoming Practical
The most important Q4 2026 takeaway is that zero-knowledge proofs are no longer just a specialized Layer 2 scaling technique. They are becoming a broader verification layer for Ethereum-style systems, while privacy-focused uses are moving closer to practical applications. For builders and investors, that means the question is shifting from “Will ZK work?” to “Which ZK architecture solves this specific problem at an acceptable cost, latency, and trust model?”
On the scalability side, Ethereum’s roadmap now treats zkEVM work as a path toward verifying Layer 1 execution itself, not only rollups. On the privacy side, current roadmaps increasingly emphasize private proving and selective disclosure rather than blanket anonymity. These are separate use cases that share proving technology but have different product requirements.
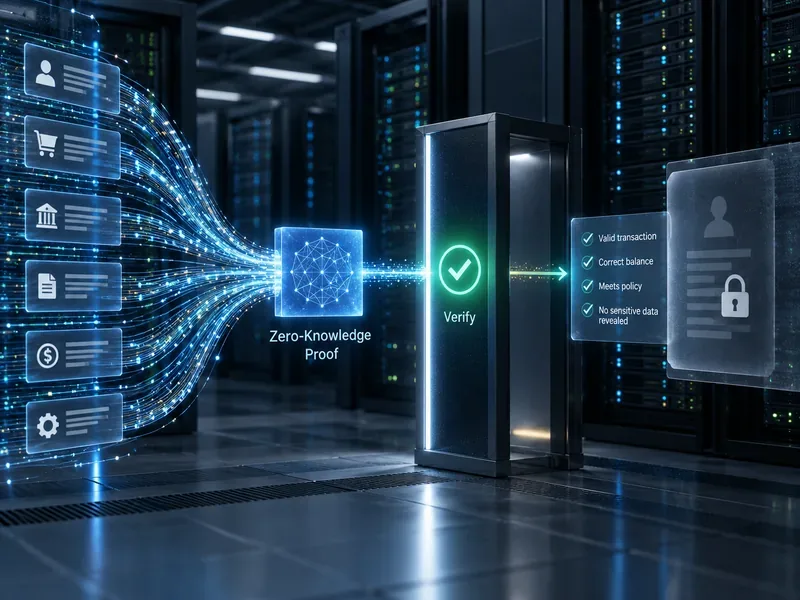
A zero-knowledge proof can let a verifier confirm that a rule was satisfied without receiving the underlying private data; the same proof-compression idea can also reduce the amount of computation that must be repeated by blockchain verifiers.
Why Q4 2026 matters for zero-knowledge proofs
The clearest trend is a widening of the ZK design space. Ethereum’s official zkEVM roadmap describes a future in which a specialized prover executes an Ethereum block and creates a succinct proof, allowing nodes to verify that proof instead of re-executing every transaction. The page, updated June 24, 2026, identifies real-time proving, execution-client integration, and sustainable prover economics as active tracks. See the Ethereum zkEVM roadmap.
This does not mean Ethereum validators have already stopped re-executing blocks. It means ZK is being developed as possible core infrastructure. The distinction matters: today’s production ZK rollups and tomorrow’s L1 execution proofs solve related but different problems.
For Q4 planning, the useful conclusion is straightforward: ZK scalability is becoming more infrastructural, while privacy is becoming more application-specific.
Trend 1: ZK scaling is moving from rollups toward Layer 1 verification
ZK rollups remain one of the most established uses of validity proofs. They execute transactions offchain, batch them, and submit a proof that the resulting state transition is correct. Ethereum’s documentation explains that this can reduce repeated computation and improve capital efficiency because withdrawals do not require an optimistic challenge period. See Ethereum’s zero-knowledge rollup documentation.
The newer development is the push to use zkEVMs for Ethereum block verification itself. The Ethereum Foundation reported in late 2025 that participating systems had crossed an important real-time proving threshold, with leading zkVMs able to prove the overwhelming majority of blocks within a single Ethereum slot on target hardware. The Foundation then shifted emphasis toward security, proof size, and integration rather than raw speed alone. Its current 2026 protocol priorities continue to describe zkEVM as a staged path from optional execution proofs toward proofs becoming expected and eventually mandatory. See the Ethereum Foundation’s September 2026 protocol priorities.
Who should care? Infrastructure teams, rollup developers, node implementers, and projects building verifiable compute should watch this closely. A consumer app that only needs cheaper transactions does not need to design around future L1 proving today.
Trend 2: Recursive proving is becoming a practical scalability primitive
Recursive proofs allow one proof to attest to the correctness of other proofs. Instead of verifying many independent proofs onchain, a system can aggregate them into a smaller number of final proofs. This is valuable when throughput grows because verification overhead can be amortized across many batches, chains, or application computations.
Starknet has used recursive STARK proving in production for years, and its 2026 roadmap continues to treat proof systems as a core scaling engine. More recently, Starknet’s September 2026 prerelease notes for v0.14.4 describe support for proving a block-sized single transaction through the SNIP-36 client-side proving flow, subject to stated execution constraints. The planned mainnet date is October 5, 2026, pending governance approval. Because that date is still conditional as of this article, it should not be treated as a completed mainnet upgrade. See the Starknet v0.14.4 prerelease notes.
When does recursion fit? It is attractive when many proofs must ultimately settle to the same verifier, or when expensive computation can be split into parallel proof jobs and compressed later. It is less compelling when the workload is small enough that direct execution is cheaper and operationally simpler.
Trend 3: Privacy is shifting from “hide everything” to selective disclosure
Privacy is often discussed as if a blockchain application must choose between total transparency and total anonymity. The emerging model is more nuanced. Ethereum’s privacy roadmap, updated August 24, 2026, identifies private reads, private writes, and private proving as separate problems. It explicitly frames privacy as selective disclosure: proving a fact without disclosing all the underlying data. See the Ethereum privacy roadmap.
A practical example is age or eligibility verification. An application may need to know that a user is over a required age, belongs to an approved group, or satisfies a balance threshold. A ZK proof can potentially verify the condition without publishing a birth date, identity document, complete credential set, or account history.
This approach is especially relevant to identity, payments, institutional finance, games with hidden information, and applications where public state would reveal commercially sensitive behavior.
Important limitation: succinct does not always mean private
One of the easiest mistakes is assuming every zkVM automatically hides inputs. Ethereum’s privacy documentation warns that many systems commonly called zkVMs are primarily succinct: they produce compact proofs that are cheap to verify, but they do not necessarily provide the hiding property needed for privacy applications. Developers need to verify the actual zero-knowledge properties of the proving system and its implementation rather than relying on the “zk” label.
Trend 4: Private smart contracts are moving closer to usable applications
Aztec provides one concrete example of the privacy-first direction. Its Alpha V5 update, announced July 21, 2026, says private-transaction proving time was reduced by more than two times versus the prior version and that the cost of a fully private transaction was reduced by roughly half. The same release describes early privacy-preserving applications running on the network. See Aztec Alpha V5.
Aztec’s broader design combines private and public execution so developers can decide which data and logic must be public and which can remain private. It also emphasizes selective disclosure for cases such as compliance, tax reporting, and delegated permissions. See The Aztec Stack.
Who is this for? Applications that genuinely lose value when all state is public. If a normal public smart contract already meets the product requirement, adding private state introduces proving, key-management, wallet, debugging, and compliance complexity that may not be justified.
Trend 5: Prover performance is no longer the only benchmark that matters
Raw proof-generation speed remains important, but Q4 evaluation should include security assumptions, hardware concentration, proof size, verifier cost, latency distribution, and whether the system depends on a trusted setup. The Ethereum Foundation’s real-time proving work has increasingly emphasized security requirements and machine-checked cryptographic analysis after major performance gains.
This changes how teams should compare ZK stacks. A faster prover is not automatically the better production choice if it requires extreme hardware, has weaker security assumptions, produces oversized proofs, or cannot meet the application’s privacy requirements.
Use case
What ZK is doing
Best fit when
Watch out for
L2 scaling
Proves batched state transitions
You need lower transaction cost and Ethereum settlement
Sequencer centralization, data availability, proving cost
L1 execution verification
Proves correct block execution
You are building core infrastructure or verifiable execution systems
Security, integration maturity, prover economics
Private identity or credentials
Proves a fact without revealing the source data
You need selective disclosure
Credential trust, revocation, metadata leakage
Private smart contracts
Hides selected state or computation while proving correctness
Public state would expose sensitive user or business activity
You settle many proof-producing workloads to a shared verifier
Added prover architecture and latency complexity
How to decide whether ZK is the right solution
Start with the problem rather than the cryptography. ZK is a strong fit if you need one of three things: verification without re-execution, verification without revealing private inputs, or aggregation of many independently proven computations. If you do not need one of those properties, conventional execution, signatures, access control, or database privacy may be simpler.
Choose a ZK rollup when settlement security matters more than operating your own chain
If your product mainly needs cheaper execution with Ethereum settlement, a mature rollup may be more appropriate than designing a custom proving system. The application inherits an existing sequencer, bridge, prover, and developer environment rather than owning the entire stack.
Choose application-level private proving when disclosure is the actual problem
If the core requirement is “prove this user qualifies without exposing their underlying information,” do not automatically move the entire application into a private execution environment. A narrowly scoped proof can reduce architectural complexity and make audits easier.
Choose a private execution environment when hidden state is central to the product
Private balances, sealed bids, confidential trading logic, private governance actions, and hidden-information games can require more than one isolated proof. In those cases, a network or framework designed around private state may be a better fit than adding one-off circuits to a public application.
What to watch through Q4 2026
Ethereum L1 zkEVM integration: performance has advanced rapidly, but security, client integration, incentives, and protocol scheduling remain the gating factors.
Client-side proving: better local proving can make private identity and application actions feel more like ordinary wallet interactions, but hardware variability remains a real constraint.
Selective disclosure: this is likely to matter more to mainstream applications than generic “anonymous blockchain” messaging because it maps directly to compliance and identity requirements.
Proof aggregation: recursion and shared proving infrastructure can improve economics as more chains and applications produce proofs.
Post-quantum security research: hash-based proof systems are receiving more attention as Ethereum research connects ZK infrastructure with longer-term cryptographic agility and post-quantum goals. The Ethereum Foundation’s August 2026 work on machine-checked security bounds for hash-based SNARKs is one example: Better Codes challenge.
Bottom line
For Q4 2026, the strongest ZK trend is convergence: scaling, verifiable computation, privacy, and identity are increasingly using related proof infrastructure, but they are not becoming one identical market. ZK rollups optimize blockchain execution; L1 zkEVM research targets validator verification; privacy systems focus on hiding inputs and state; selective-disclosure applications prove only the facts a verifier needs.
The right implementation therefore depends on the property your product cannot compromise on. If it is throughput, evaluate proving cost, latency, and data availability. If it is privacy, verify that the system provides genuine zero-knowledge rather than only succinct proofs. If it is institutional adoption, evaluate selective disclosure, auditability, and operational control. ZK technology is becoming more capable in all three areas, but choosing the correct trust and privacy model remains more important than choosing the most fashionable proving stack.